Edit Role
Important
Information and features vary according to the roles to which you belong and the permissions associated with those roles. For more information, contact your module manager or your campus support team.

The Edit Role page lets you manage role permissions, assigned users, access controls, and role relationships. The tabs available vary depending on the role.
Each role includes:
Name
Description
Permissions
Assigned users
Module Access settings
Association settings (if applicable)
User-Defined Form/Field permissions (if applicable)
Changes can be made at any time and are reflected for all users assigned to the role.
To update roles, you must belong to a role with the appropriate permissions enabled. Jenzabar provides these permissions with the Common, User Management role, but your school may have created a customized version of this role.
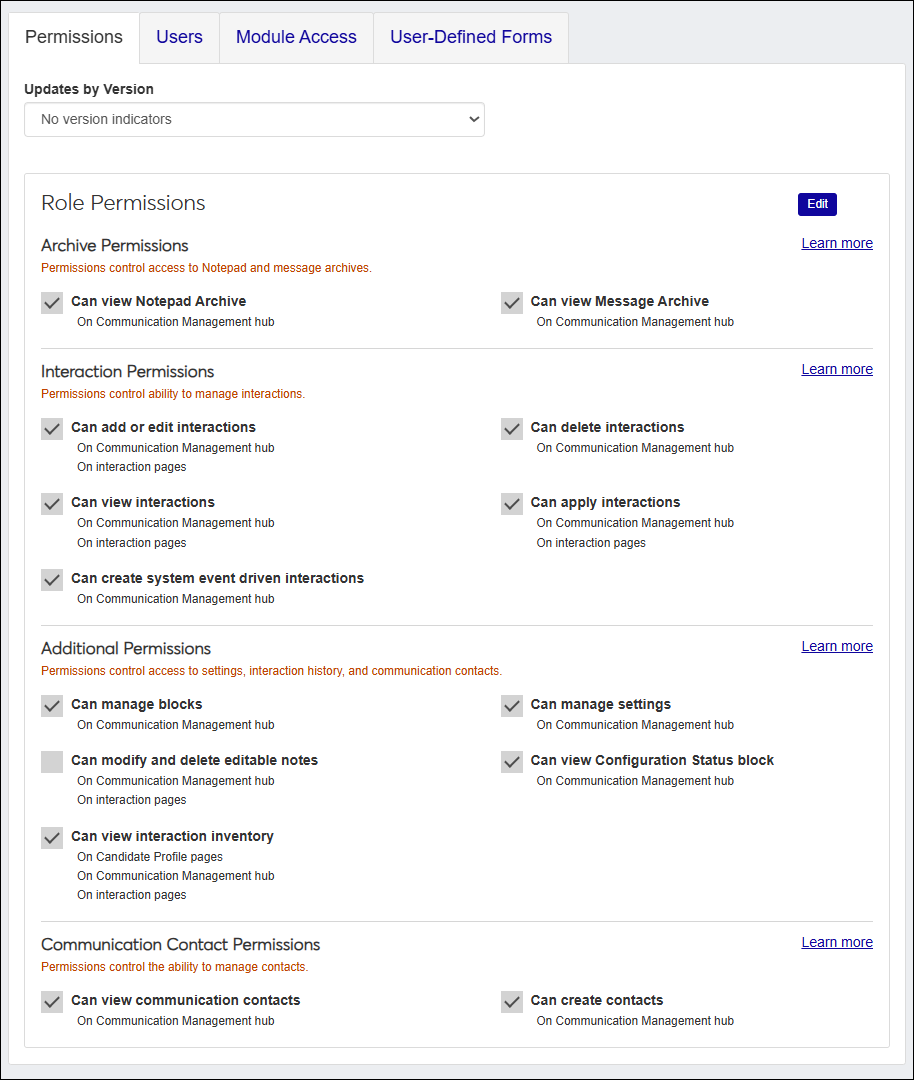
The Permissions tab controls which pages, features, and actions users can access in J1 Web. Permissions are granular, allowing users to have different levels of access to various functionalities.
Permissions are organized by module and feature area. Depending on the permission, users may be able to:
View information
Create records
Edit records
Delete records
Configure settings
Users assigned to multiple roles receive permissions from all assigned roles.
Updates by Version | Select a version to see show which roles have been added or changed and in which release. This can help identify new permissions and ensure they are enabled for the appropriate roles.
|
Permissions and Permission Checkboxes | Permissions are grouped by relevance. To enable or disable permissions, click the Edit button and select the appropriate checkboxes. Hubs and pages impacted by the permission are listed underneath. |
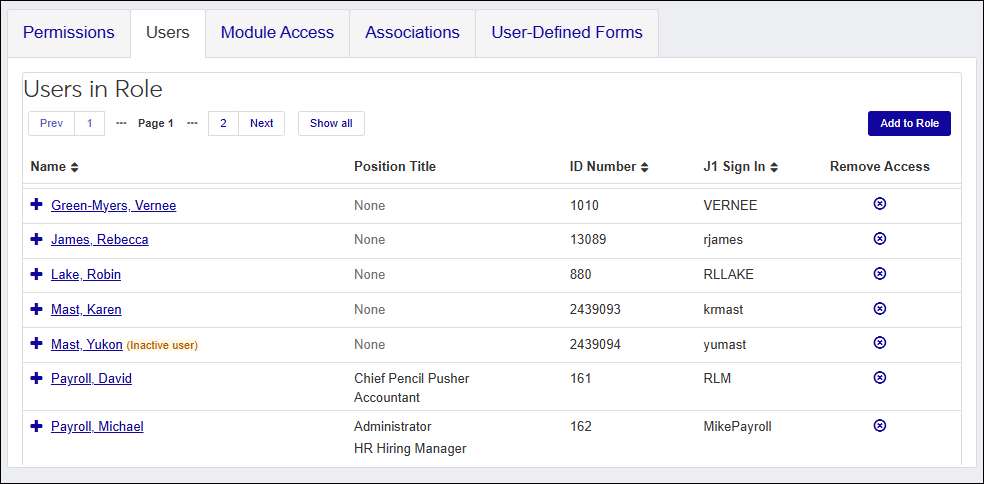
The Users tab lists individuals assigned to the role with options to add and remove users. Users can be assigned to multiple roles. To be added to a role, users must have an ID number and be an active J1 Web user.
Note
You may see a inactive user listed, which means they were deactivated after being added to the role. Only active users can be added to roles. Inactive users are identified by the Inactive user icon  .
Name |
|
Position Title | Shows any titles a user is assigned to on the Positions tab in the Desktop HR Employee Master via Personnel window. If the user is not assigned to a position title or your school is not licensed for HCM, nothing appears in this column. |
ID Number | System identification number. |
J1 Sign In | User's J1 ID managed in the Desktop, Users window. |
Remove Access | Option to remove the user from the role. |
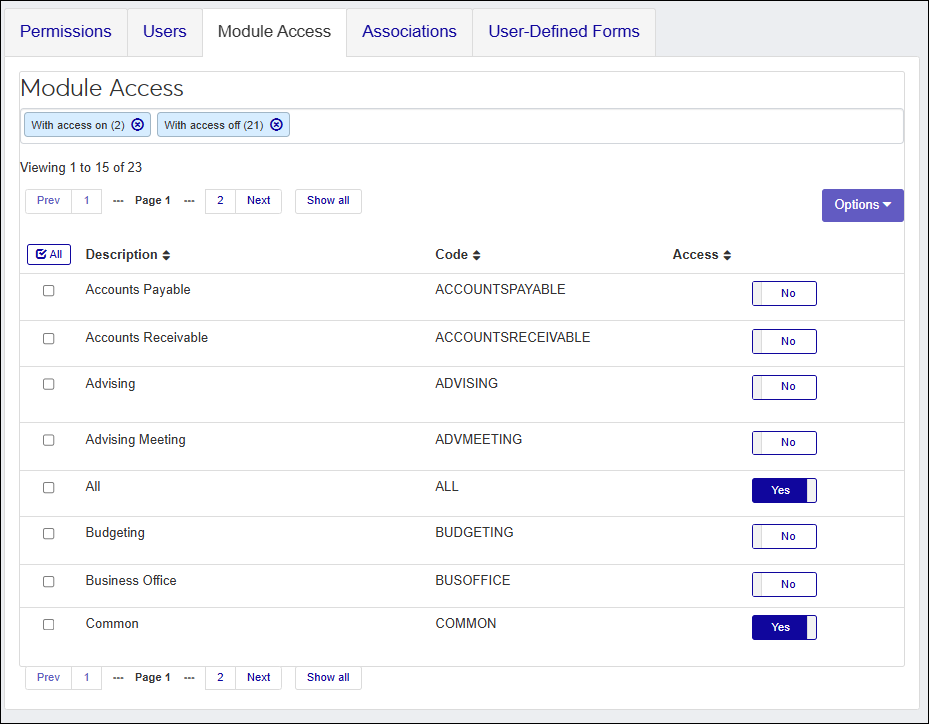
The Module Access tab controls access to different things in the system such as data sets, forms, interactions, and workflows, similar to Desktop's Module Code Stamps. Codes are associated with items throughout the system when they are created and updated. Users gain access through the roles assigned to them and the access codes enabled for each. Users assigned to multiple roles have access to the access codes enabled with each.
The following example shows interaction access codes being associated with a text interaction. Users in roles with access to the enabled codes will be able to view/work with the text message.
 |
This example shows the access code being associated with a new workflow. Users in roles with access to the enabled codes can view the workflow.
 |
Jenzabar provides access codes based on Jenzabar modules; custom codes can be created on the Access Codes page.
Description | Identifies the access code. |
Code | Access code identifier. |
Access | Enables or disables users' access to items in the system associated with the module code. If Registration access is enabled and then selected when creating interactions, users in a role with Registration access enabled can view/work with the interaction. Consider what departments would benefit from seeing different interactions, information, and workflows with students or staff. For example, advising users might benefit from being able to view/comment on student life interactions. |
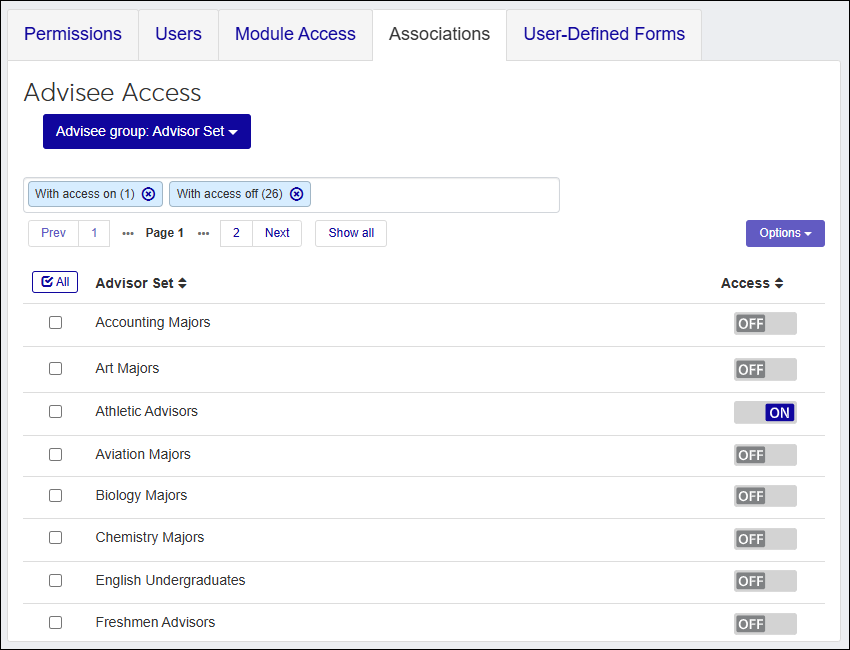
The Associations tab manages relationship-based access. It is only available for select roles, and options vary by role. As relationships change, access is updated automatically.
Examples: A coach may receive access to students based on athletic roster membership. When a student is added to or removed from a roster, access is updated accordingly. Department Heads can have access to students based on their majors. When a student adds or changes a major, the Department Head's access is updated automatically.
Group selector | Groups available for access. Groups are categorized by concentration or program, budgets, advisor sets, etc. you created in your system. Users in the role will be able to access individuals/things in the group based on the enabled sets. |
Set | Lists the criteria that drives the association. For example, lists all available advisor sets, budgets, concentrations and programs. |
Access | Enables or disables users' access to the group. If the Advisor Set access is enabled for Athletic Advisors, then users will see advising information for student athletic advisors. |
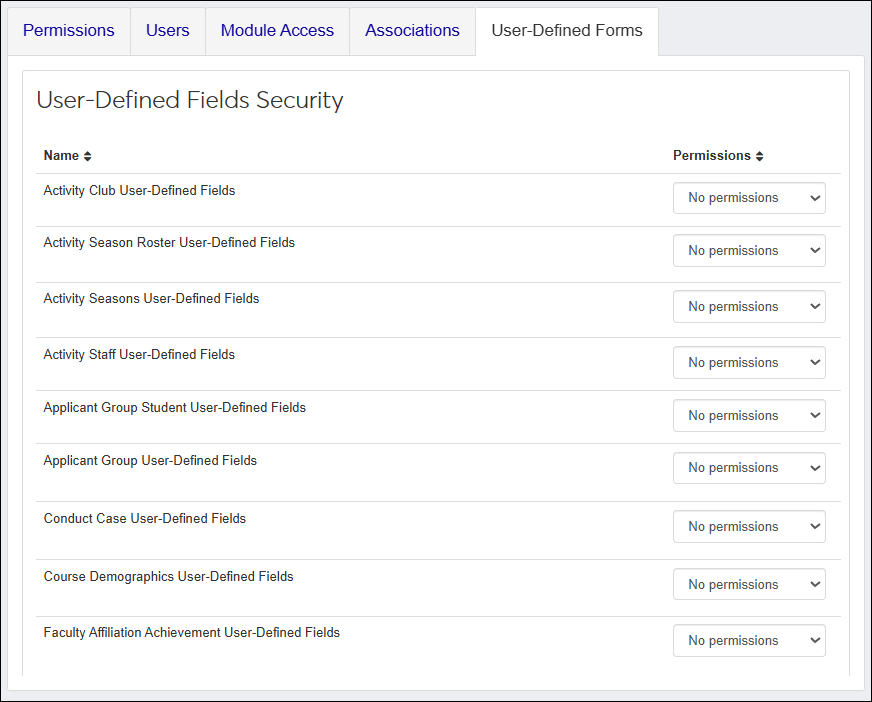
The User-Defined Fields tab controls permissions for viewing, editing, and configuring user-defined fields (UDEF) across the system. Users who belong to multiple roles will have access to the user-defined features enabled with each.
Permission levels determine what users can do with user-defined fields:
No permissions - users cannot see/access this user-defined field.
Can view UDEF data - users can see this user-defined field but cannot modify it.
Can edit UDEF data - users can view, update, and delete data in this user-defined field.
Can configure UDEF form - users can configure this user-defined field and includes view and edit permissions. They can also manage the fields from the Manage User-Defined Fields page.


Tip
To review detailed information about the role permissions, refer to the Jenzabar-Provided Roles online help topic.
Access the System Roles page.
Find the appropriate role. You can use filter and sort options to help.
From the Options menu, select Edit. The Edit Role page appears.
Select the Permissions tab.
Click Edit. The permissions checkboxes are enabled.
Select the checkboxes of the permissions you want to grant the role or deselect the permissions you want to remove from the role.
Note
When you assign permissions to the role, it is important to consider the different levels of capability you want users to be granted. You may want to create several roles with varying permissions to accommodate different types of users.
Click the Save button. Several things happen:
Permissions are associated with the role and the checkboxes are no longer enabled.
Role permissions are immediately applied. A user will immediately have permission granted or revoked according to the updated features of the role.
Access the System Roles page.
Find the appropriate role. You can use filter and sort options to help.
From the Options menu, select Edit. The Edit Role page appears.
Select the Users tab.
Click the Add to Role button. The Add to Role window appears.

Start typing the name of the user you want to add to the role and select them. You can select as many users as needed.
Note
Only active J1 Web users with an ID number can be added to the role. Users are activated using the Desktop, Users window. For more information, see Managing User Access to J1 Web.
Click the Add to Role button. The Add to Role window closes and the Edit Role page appears with the newly added user shown in the list. Additional user information is available by clicking the Expand icon.
Access the System Roles page.
Find the appropriate role. You can use filter and sort options to help.
From the Options menu, select Edit. The Edit Role page appears.
Select the Users tab.
Click the Remove icon
 in the Remove Access column. The confirmation pop-up window appears.
Click the Yes, remove button. The confirmation pop-up window closes and the Edit Role page reappears with the user no longer listed.
To view a user's Desktop ID Number and Sign In, and a list of any other roles the user is assigned to, click the Expand icon.
Note
Use the column headings to quickly sort the listings.
Tip
Jenzabar provides access codes based on Jenzabar modules; custom codes can be created on the Access Codes page.
Access the System Roles page.
Find the appropriate role. You can use filter and sort options to help.
From the Options menu, select Edit. The Edit Role page appears.
Select the Module Access tab.
From the Access column, click the OFF or ON option to enable or disable access to the appropriate module access codes. These access codes are associated with items and information throughout the system and users with the code enabled will have immediate access to it. If a user belongs to multiple roles, they’ll have access to the items available with each.
Only available with certain roles.
Access the System Roles page.
Find the appropriate role. You can use filter and sort options to help.
From the Options menu, select Edit. The Edit Role page appears.
Select the Associations tab.
From the Group drop-down, select the appropriate group. The groups appear.
Notice
For example, the Secondary Advisor - Access to Students by Academic Program role groups students by certifications, concentrations, minors, and programs. Once you select the certifications group, you'll see a list of the available certifications.

From the Access column, click the OFF or ON option to enable or disable access. Users assigned to the role will have immediate access to individuals in the group based on their association to them.
If an individual moves out of the group, the user assigned to the role no longer has access to them through this role and group. This could be when a student is no longer on a coach's roster or a student changes majors and their advisor changes.
Only applies to schools using user-defined information in the system.
Access the System Roles page.
Find the appropriate role. You can use filter and sort options to help.
From the Options menu, select Edit. The Edit Role page appears.
Select the User-Defined Forms tab. User-Defined Fields Security information appears.
From the Permissions drop-down for the various fields, select from the following permission options:
No permissions - users cannot see/access this user-defined field.
Can view UDEF data - users can see this user-defined field but cannot modify it.
Can edit UDEF data - users can view, update, and delete data in this user-defined field.
Can configure UDEF form - users can configure this user-defined field and includes view and edit permissions. They can also manage the fields from the Manage User-Defined Fields page.
Access the System Roles page.
Locate the role to review.
Click the Edit icon next to the role. The Edit Role page appears.
From the Updates by Version drop-down on the Permissions tab, select the version for which you want to see information about new and updated roles.
New and Updated indicators appear next to roles that were added or changed for the selected release version.
New means the role was added to J1 Web in the release shown.
Updated means the role was changed in the release shown. This could mean permissions were added or modified.
Note
Removed roles and permissions are not shown at this time.
Yes, click the Expand icon. The user's Desktop login, ID, and other J1 Web roles appear.
Yes, you can remove and grant access to the same user as many times as needed. Follow the How Tos listed above for step-by-step instructions on adding a user to a role and removing a user from a role.
Yes, any users assigned to a role can immediately access all the information and features associated with the role. You can create several similar roles with varying levels of access to control access for different users.
Ensure you clicked the Edit button before updating the role permissions. If you still cannot update the role permissions, you may not have access to the edit feature. For some roles, various permissions are enabled by default as part of the selected role template and cannot be changed.
They may not have been added to the Desktop application. This can be verified using the Desktop Users window.
Users can be added in J1 Web if they are informally associated with a process, but they cannot log in to J1 Web and are not considered active J1 Web users. In order to be assigned to a role in J1 Web, they must be in the Desktop application and have an active J1 Web login (designated on the Desktop Users window).
Several things could cause this happen:
The user may be in the Desktop application, but doesn't have an active J1 Web login.
The user may have been added to J1 Web and not the Desktop application.
The user may be in the Desktop application, but doesn't have an active J1 Web login.
The user may already be assigned to this role.
To resolve this issue:
Verify the user exists on the Desktop Users window.
Verify the user has an active J1 Web login on the Desktop Users window.
Verify the user isn't already assigned to the role by searching for them in the Filter these users search option.
What are active users?
Active users have an active J1 Web login and can be assigned to roles. Users are activated on the Desktop, Users window.
Can a user belong to multiple roles?
Yes. Users can be assigned to multiple roles and receive access from each assigned role.
Position titles are assigned to users on the Desktop HR Employee Master via Personnel window, Positions tab. If the user is not assigned to a position title, nothing appears in this column.
Your school may not be licensed to use the Human Resources module.
The user may not be assigned to a position on the Desktop HR Employee Master via Personnel window, Positions tab.
Some permissions are selected and can't be deselected because another permission depends on them. For example, granting course overrides depends on being able to view them. Therefore, you can't deselect the "Can view course overrides" permission if "Can grant course-full overrides" is selected.
Version indicators show you which roles have been added or changed and in which release. This can help you identify new permissions and ensure they are enabled for the appropriate roles.
Use the Updates by Version drop-down to select a specific version, all versions, or no versions.
New means the role was added to J1 Web in the release shown.
Updated means the role was changed in the release shown. This could mean permissions were added or modified.
Note
Removed roles and permissions are not shown at this time.
New permissions may become available following a software update. Administrators can review and enable those permissions as needed.
Jenzabar provides access codes based on Jenzabar modules; however, you can create custom codes on the Access Codes page. Select Core from the main navigation pane, then select Campus-wide Definitions, and then Access Codes.
Only roles that support relationship-based access include the Associations tab.
The highest level of access assigned through any role is applied to the user.